Stay ahead in the age of AI agents
At nerl0 we explore how AI agents and non-human identities change who can reach your data, and we build the tool to keep that visible. Read what we learn about access, evidence and fixing what matters first.
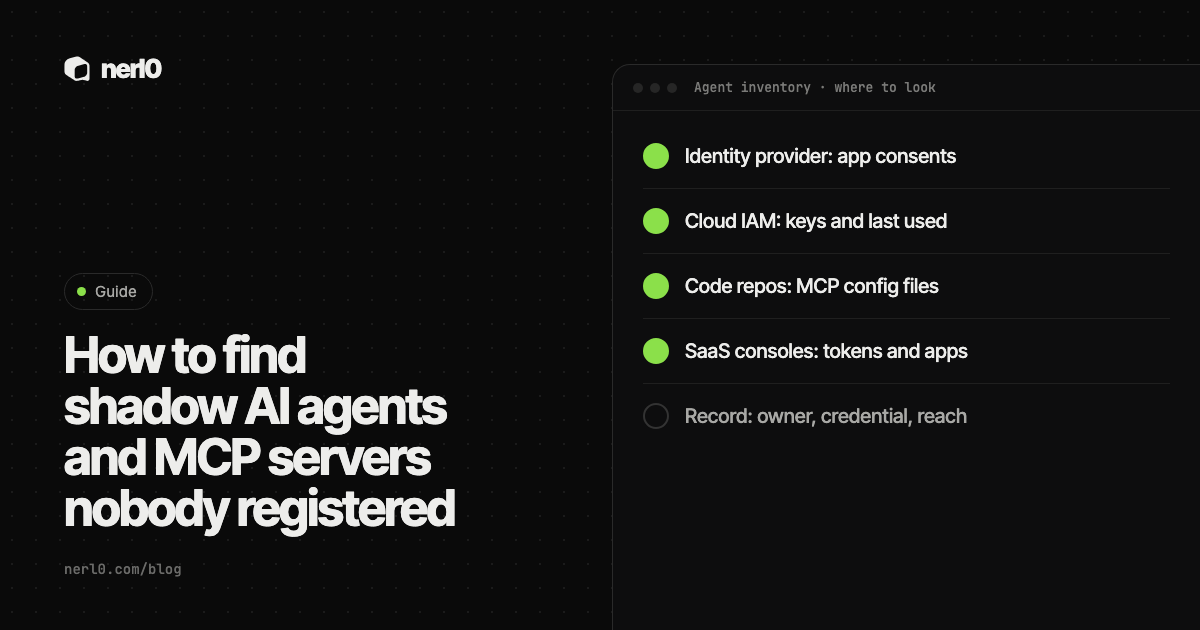
How to find shadow AI agents and MCP servers nobody registered
Nobody registered them, but they hold real access. Four places to look, and the four facts to write down for every agent you find.
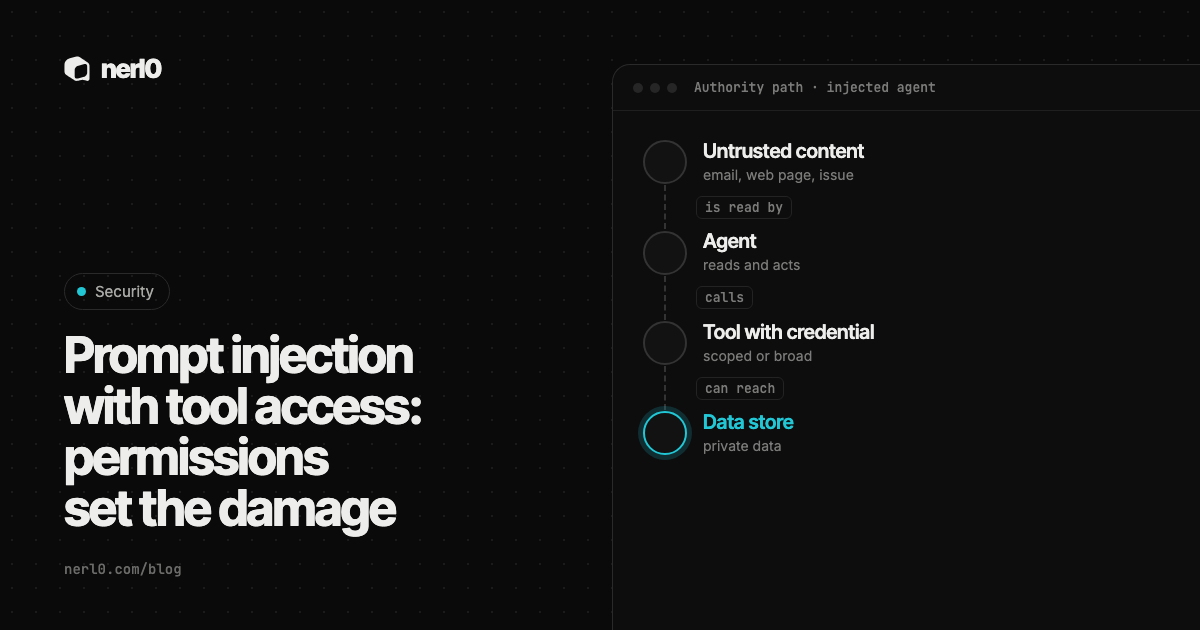
Prompt injection with tool access: permissions set the damage
You cannot promise that an agent will never follow a planted instruction. You can decide what it is able to do when it does.
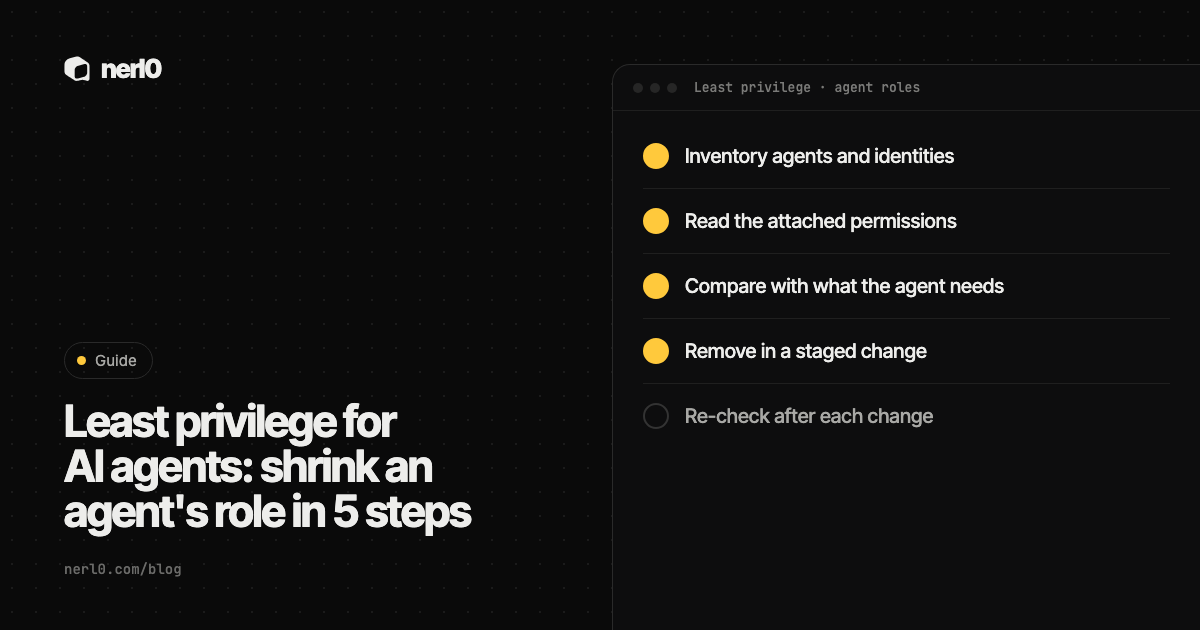
Least privilege for AI agents: shrink an agent's role in 5 steps
Agent roles start broad and stay broad. A five-step routine to inventory them, compare them with real use, and cut them back safely.
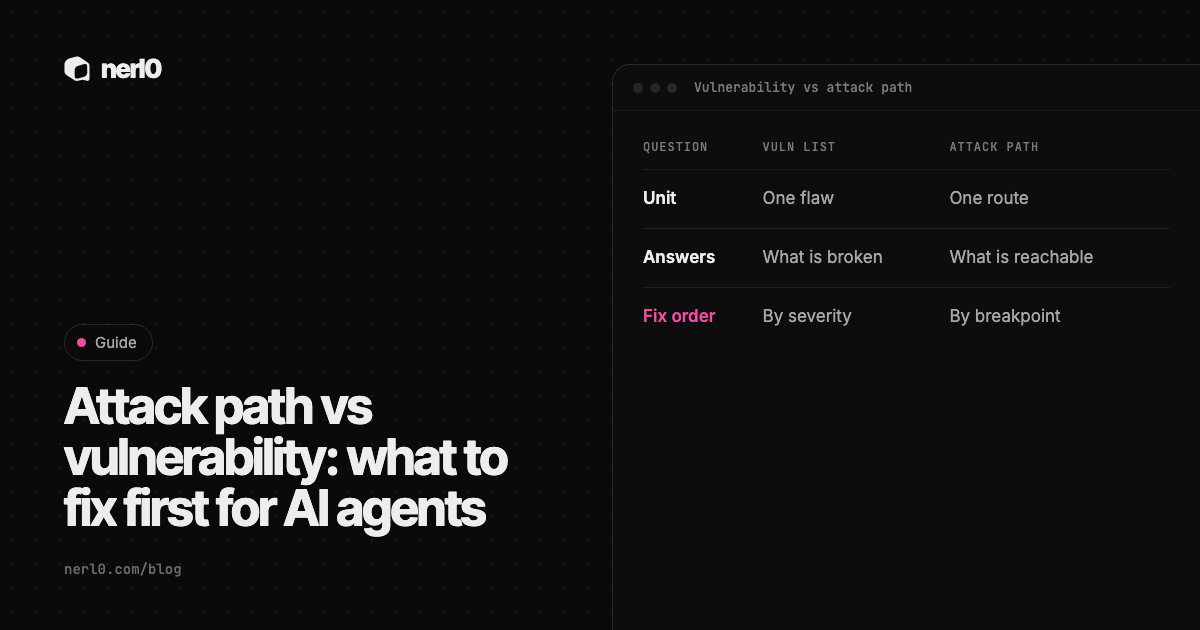
Attack path vs vulnerability: what to fix first for AI agents
A CVE list tells you what is broken. A path tells you what an agent can actually reach. Why paths are the better unit for agents with standing permissions.
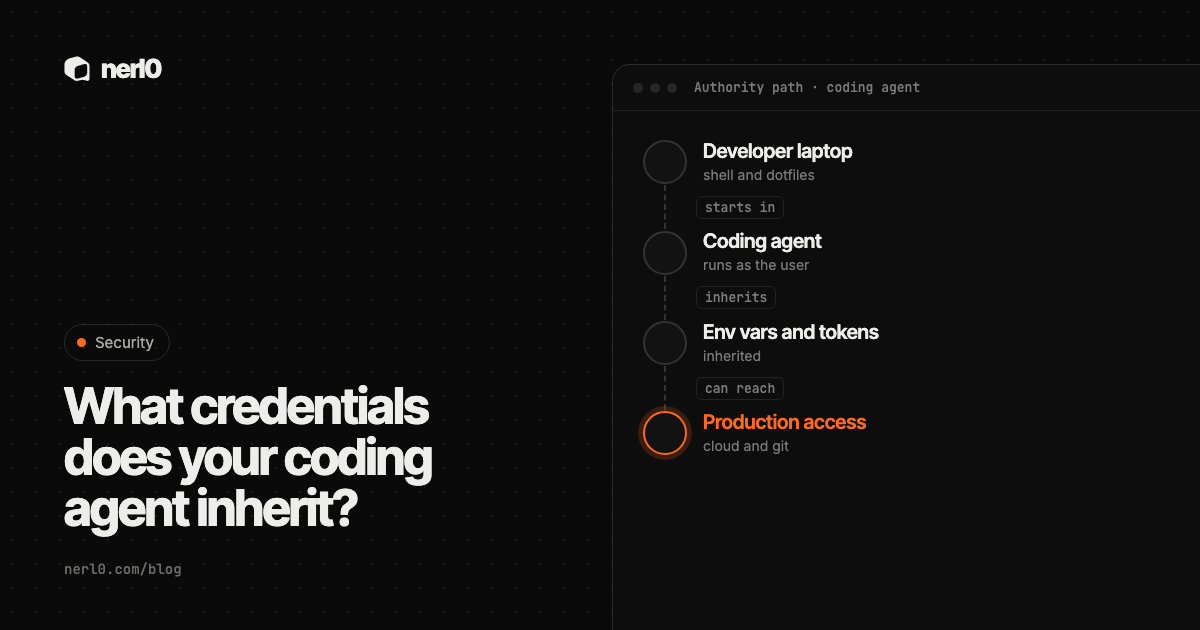
What credentials does your coding agent inherit?
The agent did not ask for your keys. It started in your shell. A practical look at what a coding agent inherits and how to narrow it.
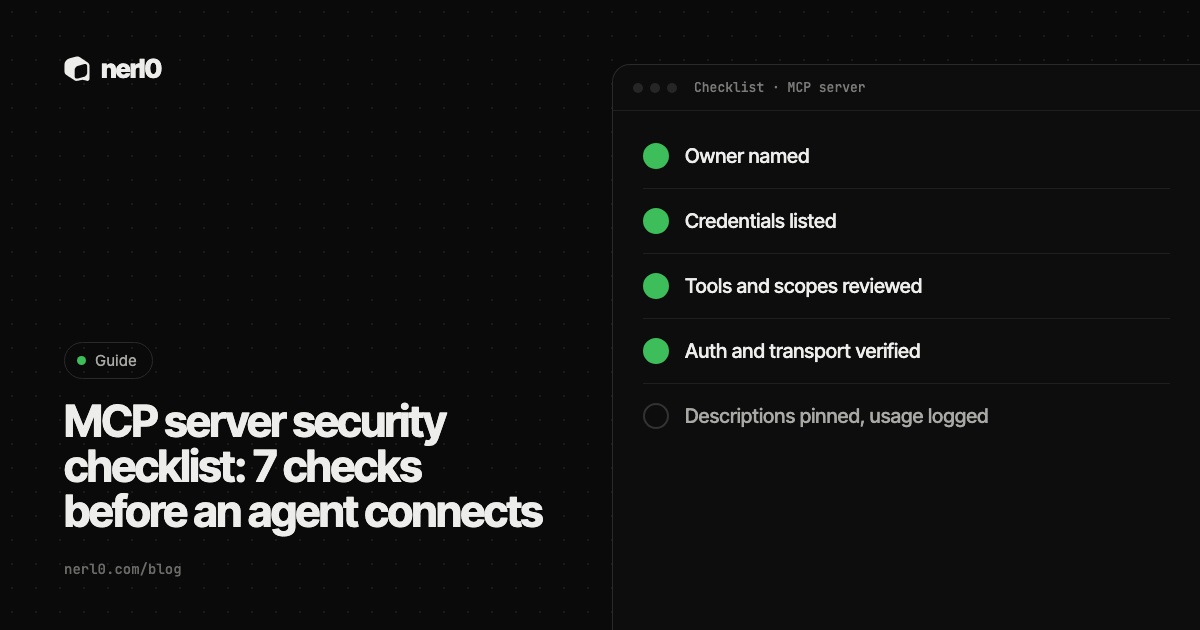
MCP server security checklist: 7 checks before an agent connects
An MCP server is a doorway with credentials behind it. Seven questions to answer before an agent walks through, each tied to the MCP spec, OWASP or researcher write-ups.
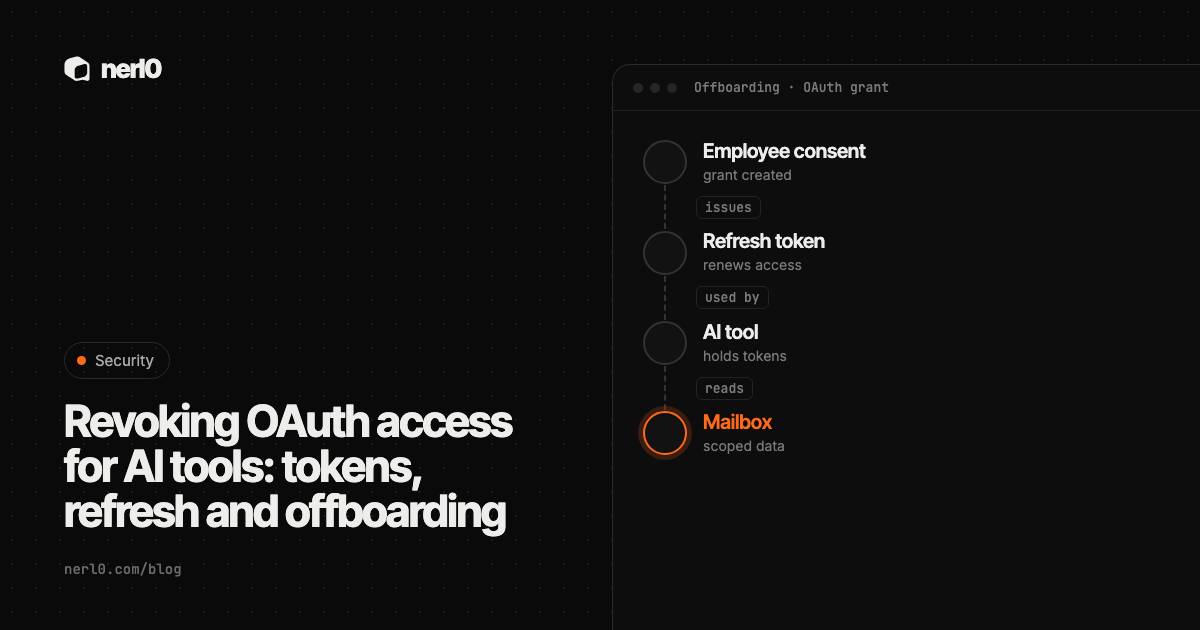
Revoking OAuth access for AI tools: tokens, refresh and offboarding
Consent creates a grant, a refresh token and access tokens. Which of them survive when an employee leaves or an AI tool is dropped, and how to revoke each one.
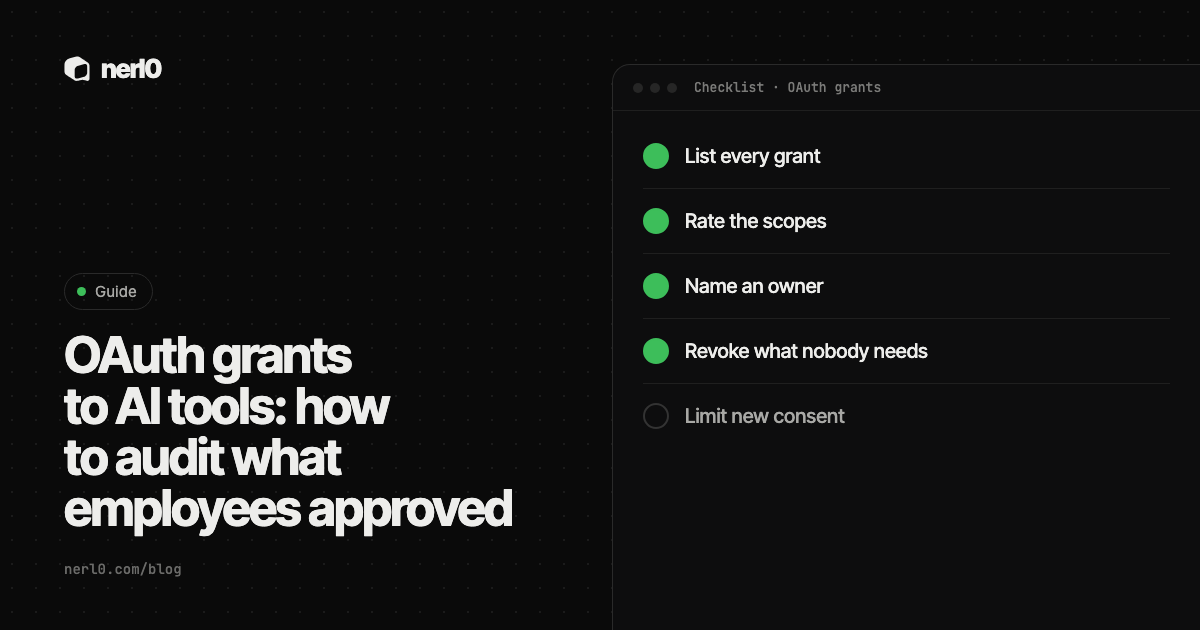
OAuth grants to AI tools: how to audit what employees approved
An employee clicks Allow once and an AI tool can reach their mail or files long after they stopped thinking about it. A practical audit for Microsoft Entra and Google Workspace.
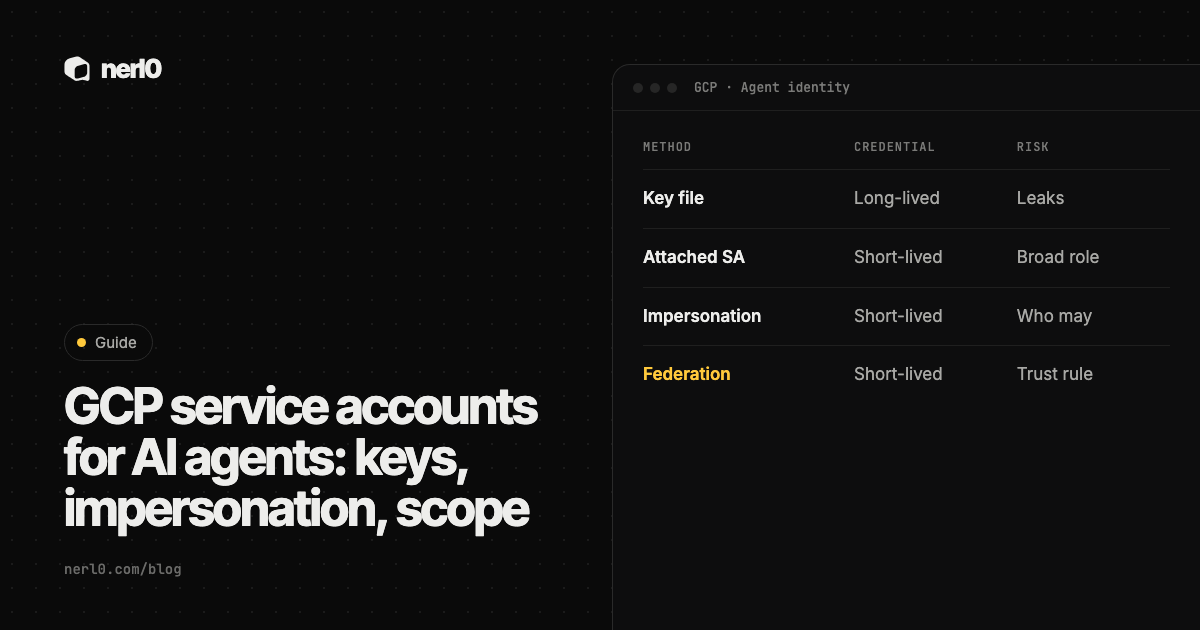
GCP service accounts for AI agents: keys, impersonation, scope
On Google Cloud, an agent's identity is a service account, and its reach is whatever roles that account holds. Four ways to give it one, and what to review.
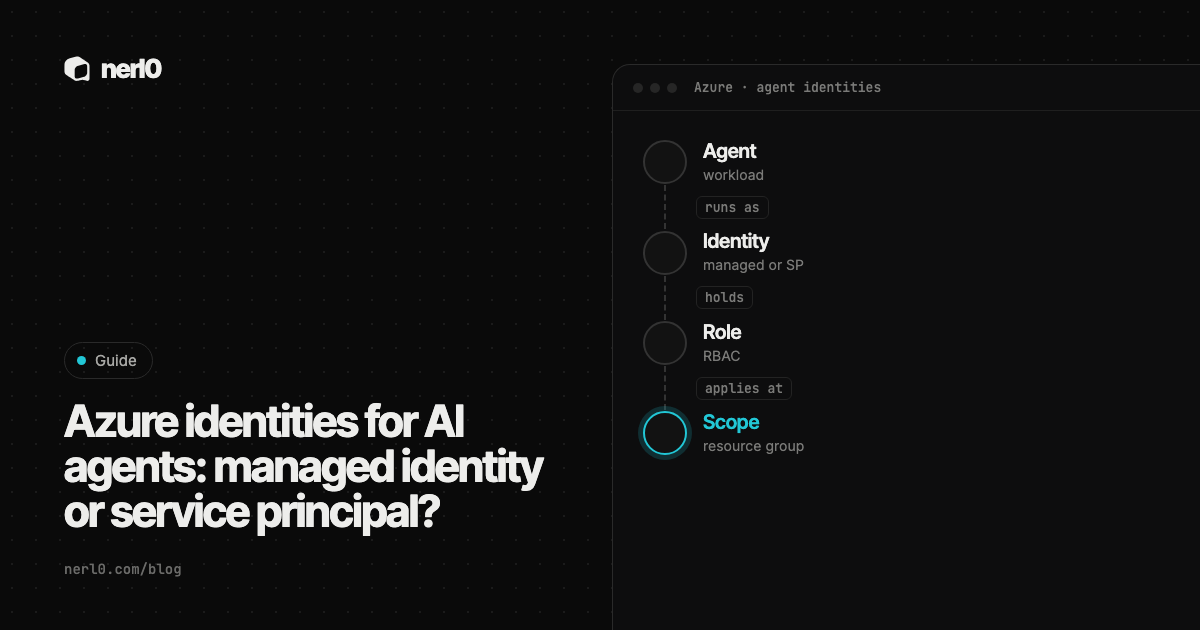
Azure identities for AI agents: managed identity or service principal?
Three kinds of identity can sit behind an agent on Azure. They differ in who holds the credential, who owns the identity and how long it lives. A comparison and a review routine.
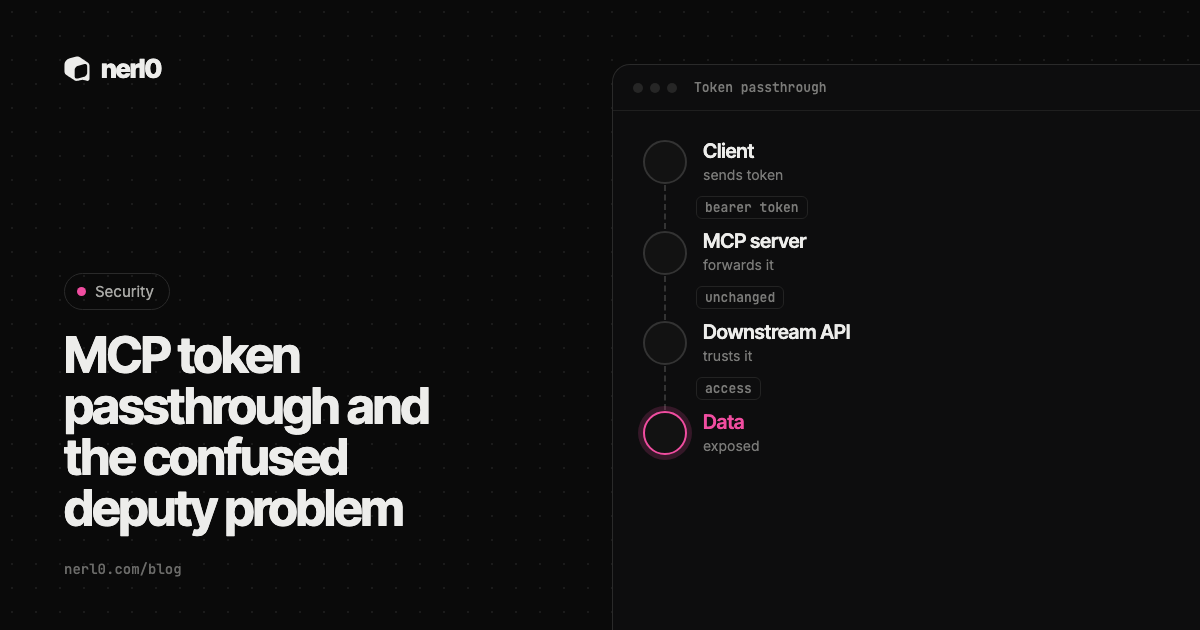
MCP token passthrough and the confused deputy problem
An MCP server that forwards the token it was handed is a deputy that never checks who is asking. What the spec requires, and five checks per server.
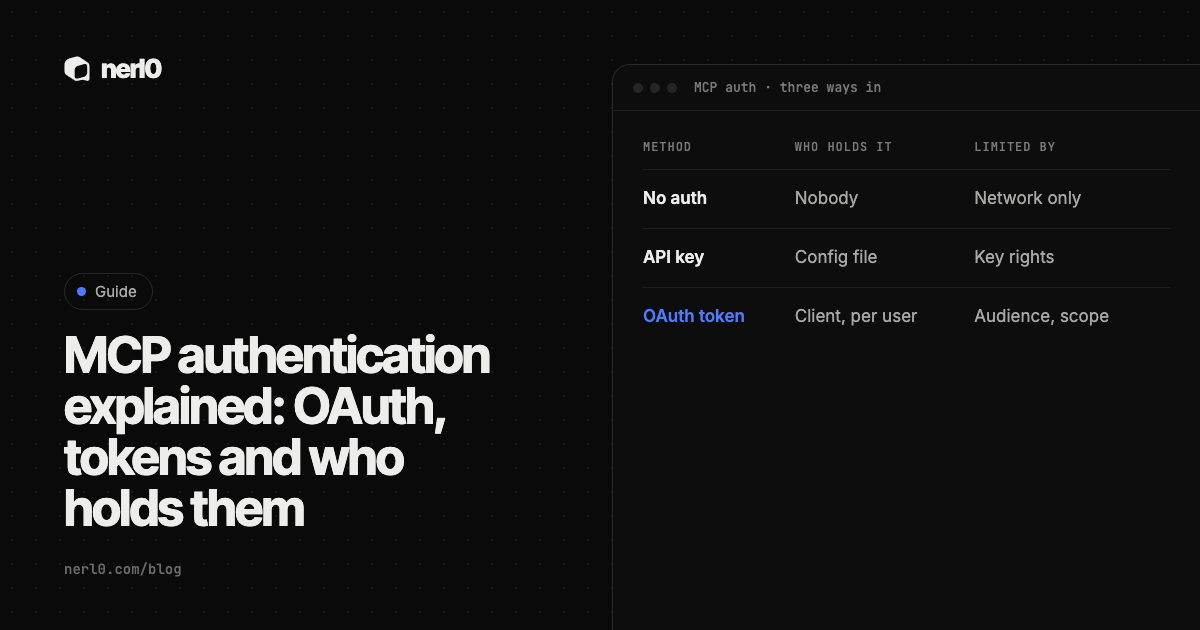
MCP authentication explained: OAuth, tokens and who holds them
MCP authorization is optional, and the way a server authenticates decides who holds the keys. How the OAuth flow works, how it differs from a pasted API key, and what to ask.
What a non-human identity is, and why AI agents make it urgent
Service accounts, API keys, OAuth apps and AI agents act in your company without a person behind them. What they are, and how to see what each one can reach.
MCP servers: the doorway with credentials behind it
To an AI agent, an MCP server is a list of tools. Behind that list sits the credentials it needs to act. What to look for, and what to ask about each server.
Activity
A route is not proof of use
Granted authority and observed activity are different things. Why every answer says what it cannot show, and how to act on a route without crying breach.
Connectors
IAM roles, keys, Lambdas and agents that can reach your buckets, secrets and databases
GitHub Apps and AI agents that can write to your repositories

Slack apps and bots, and the channels they may reach

OAuth service apps and API tokens that hold admin authority
Service accounts and API keys that can act in your projects
 P▦
27 more connectors across cloud, code, identity and AI
Read-only by default
Why nerl0 connects to your platforms through their own interfaces and never needs write access, and what that means for what it can and cannot see.
How to read the Security Graph in five minutes
Follow one authority path from an AI agent through roles and credentials to a crown-jewel secret, and learn what every label on the way means.